
Case study — SaaS
Security Testing an Encrypted App
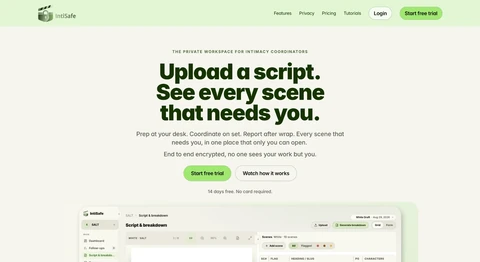
End-to-end encrypted web and mobile workspace for intimacy coordinators in film and TV, with offline sync.
Project overview
- Client
- Encrypted production-workflow app (US)
- Industry
- SaaS
- Services
- QA Testing, Web Development, Mobile Development
- Focus
- Security Testing
QA Labs worked with a US company building an end-to-end encrypted workspace for film and TV productions, focusing on security testing across web and mobile.
About the client
The client's product is a workspace for intimacy coordinators working on film and TV productions. It covers the workflow from script preparation through post-production: scenes are extracted from an uploaded script, director and actor sessions are summarised for the production team, and rider language is generated per scene with per-performer status tracking from draft to signed. On set, checklists and notes save offline and sync when the device is back in range, and coordinators can produce daily reports, risk assessments and exports to PDF, CSV or Excel. The same project is available on the web and on tablets and phones, and all data is end-to-end encrypted on the user's device — which makes security and sync behaviour central to quality.
Project scope
- Security testing — the focus of the engagement
- Web application
- Mobile apps (tablet and phone)
- Offline save and sync behaviour
How QA Labs approaches Security Testing
Our standard process for this type of work
OWASP-aligned vulnerability testing that protects user data and helps you pass security reviews.
- 01 Scope and threat model — Agree targets and identify the highest-risk areas.
- 02 Scan and probe — Automated scans plus manual testing of key flows.
- 03 Report findings — Issues ranked by severity with remediation steps.
- 04 Verify fixes — Retest each finding once your team has fixed it.
What we typically check
- OWASP Top 10 vulnerabilities
- Authentication, session, and access control
- API security and data exposure
- Input injection and XSS
- Dependency and configuration risks
What this type of engagement delivers
- Testing aligned with the OWASP Top 10 for web and APIs
- Manual checks of authentication, authorisation and business logic
- A prioritised findings report with severity and fix guidance
- Retesting of fixes once your team has addressed them
FAQ
What kind of product is this?+
An end-to-end encrypted web and mobile workspace for intimacy coordinators in film and TV, with offline checklists that sync when back online.
What did QA Labs cover in this engagement?+
Security testing of the web and mobile apps, alongside general QA of the product's workflows.
Can QA Labs help with security testing for a similar product?+
Yes. Every engagement starts with a free starter package: a scoping call and a short written audit of your product, with an NDA on day one. Most projects begin within 5–7 business days, with at least 4 hours of daily overlap with your team.
By Kawsher, Founder, QA Labs · Published 2026-10-10 · Updated 2026-10-11
Planning Security Testing work for your product?
Start with a free scoping call and a short written audit of your product, with an NDA on day one.
Related case studies
Digital Legacy Platform QA Testing
Private digital platform for preserving personal stories, photos, and memories.
Operations Management Platform Case Study
Operations management platform with employee, vehicle, inventory, and incident resource views.
No-code & Low-code Platform Testing
Talent platform for hiring no-code and low-code developers.